SEBI CSCRF Cyber Audit vs System Audit: Key Differences Explained
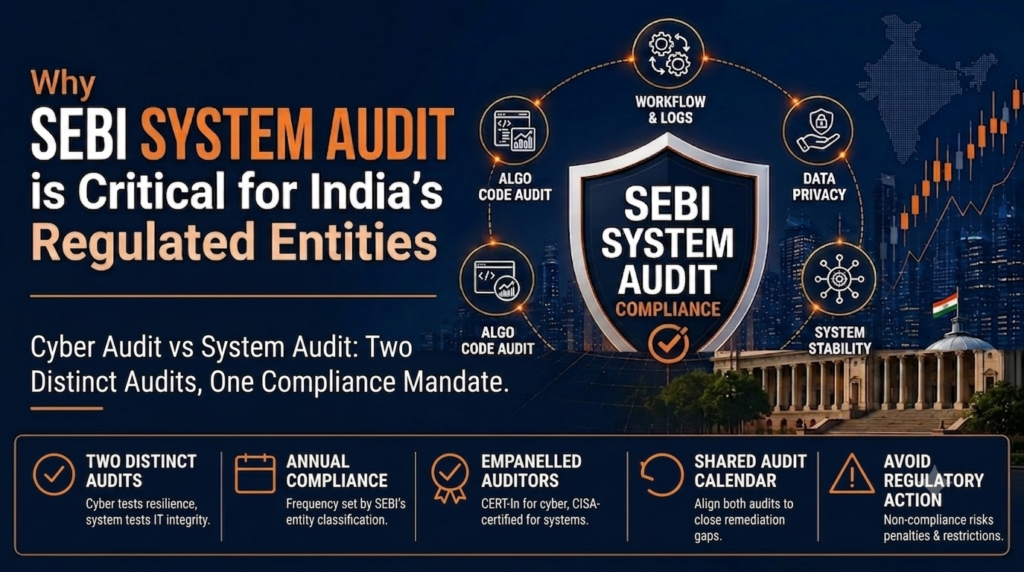
What Is the SEBI CSCRF Audit Requirement? The Securities and Exchange Board of India’s Cybersecurity and Cyber Resilience Framework (CSCRF) requires regulated entities — stock brokers, depository participants, mutual funds, KRAs, RTAs, and other market intermediaries — to undergo periodic independent audits that check their cybersecurity posture and the health of their IT systems. Here’s where a lot of confusion starts: this isn’t one audit. It’s two, and they’re not interchangeable. Cyber Audit — evaluates cybersecurity controls, threat readiness, and cyber resilience System Audit — evaluates IT systems, application controls, and operational integrity We regularly hear compliance teams describe these as basically the same thing, or assume that clearing one takes care of the other. It doesn’t work that way, and getting this wrong is usually where the compliance gaps start. Why Does SEBI Require Two Separate Audits? SEBI splits these audits because, at their core, they’re trying to answer two very different questions: Cyber Audit asks: Can this organization detect, withstand, and recover from a cyberattack? System Audit asks: Are this organization’s IT systems, applications, and processes functioning correctly, securely, and as intended? You can have a system that’s functionally rock-solid but cybersecurity-weak — an application that processes trades perfectly but has no real intrusion detection sitting behind it. Or the reverse: strong perimeter defenses paired with sloppy internal controls, poor change management, or access pathways nobody’s reviewed in years. After several sector-wide cyber incidents, SEBI made clear that functional correctness and cyber resilience needed to be judged on their own terms, not lumped into one generic “IT audit.” It’s also worth noting this isn’t a uniquely Indian approach. Frameworks like NIST CSF and ISO 27001 draw a similar line between operational/system controls and dedicated cyber-risk controls, so CSCRF’s structure lines up with what regulators elsewhere have already settled on. There’s a practical reason for the split too. India’s securities market moves enormous volumes of transactions and investor data every single day, which makes it a genuinely attractive target — for opportunistic attackers and well-funded ones alike. Run one combined audit a year and you’ll struggle to give either side the depth it needs: cyber threats shift week to week, sometimes day to day, while system and process controls tend to evolve on a slower cycle tied to software releases and governance updates. Splitting the audits lets each one go deep on its own schedule instead of getting watered down into a single, generic review. How Do Cyber Audit and System Audit Differ? If you just want the differences at a glance, here you go: Parameter Cyber Audit System Audit Primary focus Cybersecurity controls & resilience IT systems & application integrity Key question answered Can we withstand and recover from a cyberattack? Do our systems work correctly and securely? Scope Network security, VAPT, incident response, threat intelligence, SOC monitoring Application controls, access management, change management, data integrity Typical auditor expertise Cybersecurity specialists, CERT-In empanelled auditors Systems auditors, CISA-certified professionals Regulatory reference SEBI CSCRF cyber resilience clauses SEBI system audit framework (SAF) provisions Frequency Generally annual (varies by entity category) Generally annual, sometimes half-yearly for high-risk entities Output Cyber resilience report with vulnerability findings System audit report with control gap findings Common overlap area Access controls, logging, monitoring Access controls, logging, monitoring One thing worth flagging: both audits touch access controls and logging, but they’re looking at the same thing through different lenses. A cyber audit wants to know whether those controls actually stop unauthorized intrusion. A system audit wants to know whether they match the roles and business processes they’re supposed to enforce. Same territory, different question. What Does a SEBI Cyber Audit Cover? A SEBI Cyber Audit typically evaluates: Vulnerability Assessment and Penetration Testing (VAPT) across networks, applications, and infrastructure Security Operations Center (SOC) monitoring capability and incident detection speed Incident response readiness — documented playbooks, escalation matrices, and recovery time objectives Threat intelligence integration and how proactively the entity identifies emerging threats Data encryption practices for data at rest and in transit Cyber crisis management plan and business continuity provisions specific to cyber events Third-party and vendor risk — especially relevant given how many SEBI entities depend on external SaaS and cloud vendors Findings generally get sorted by severity — critical, high, medium, low — and anything landing in the critical or high bucket comes with a time-bound remediation plan attached. This isn’t a report you file away and revisit next year. What Does a SEBI System Audit Cover? A SEBI System Audit typically evaluates: Application controls — input validation, transaction processing accuracy, and audit trails Access management — role-based access control, segregation of duties, and periodic access reviews Change management processes — how software updates, patches, and configuration changes are approved and tracked Data integrity and backup processes — ensuring records remain accurate, complete, and recoverable IT governance structure — policies, documented procedures, and management oversight Business continuity and disaster recovery (BCDR) planning from an operational (not purely cyber) standpoint Compliance with SEBI’s technical and operational circulars relevant to the entity’s category Put simply: the cyber audit thinks like an attacker. The system audit checks whether things actually work the way they’re supposed to on paper. How Often Must Each Audit Be Conducted? How often you’re audited comes down to how SEBI has classified your entity — Market Infrastructure Institution, Qualified RE, Mid-size RE, or Small-size RE. As a rule, the bigger and more systemically important you are, the more often you’re audited. Broadly, though: Cyber Audit: Usually annual, with some high-risk categories also required to run half-yearly VAPT cycles that feed into that annual audit System Audit: Usually annual too, typically aligned with the entity’s financial year or a SEBI-specified schedule One caveat worth repeating: these timelines shift as SEBI issues new circulars, so don’t treat any of this as gospel. Check the latest circular that applies to your entity’s classification before you build a compliance calendar around it. Who Needs to Comply? CSCRF casts a wide net across the securities market ecosystem.
Why SEBI CSCRF Compliance Services Are No Longer Optional for India’s Regulated Entities
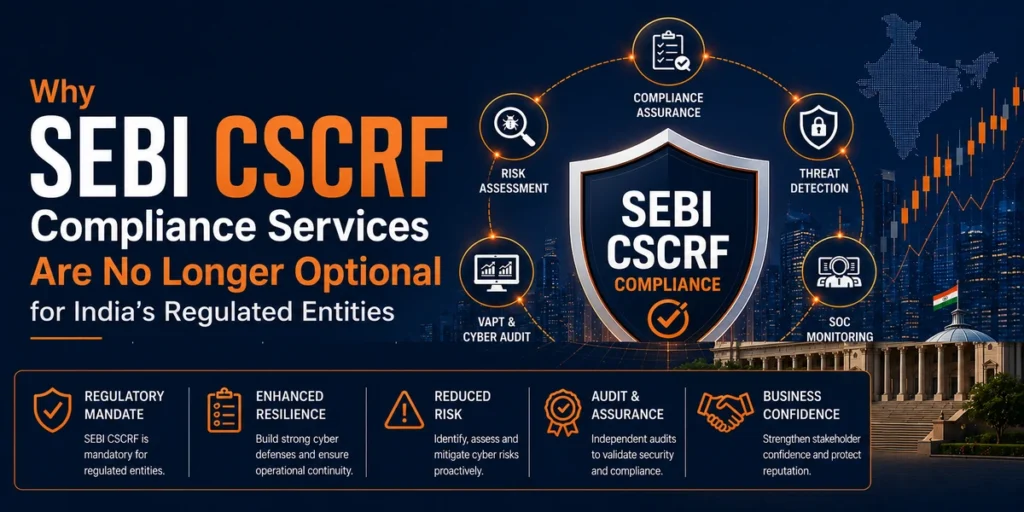
India’s securities market is under siege — not from market volatility, but from cyber threats that are growing faster than most organizations can respond to. Regulated entities registered with SEBI — brokers, depositories, AMCs, exchanges — sit at the heart of this risk. They hold sensitive investor data, process billions in daily transactions, and are increasingly targeted by sophisticated threat actors who know exactly how valuable that data is. SEBI recognized this and introduced the Cybersecurity and Cyber Resilience Framework (CSCRF) — a structured, mandatory directive that raises the bar for how every regulated entity protects itself. Yet across the industry, many organizations are still treating SEBI CSCRF Compliance services as a periodic formality rather than the ongoing operational priority it was designed to be. This blog cuts through the noise. It explains what SEBI CSCRF actually demands, why organizations struggle to meet those demands, and what a proper compliance engagement — including a SEBI CSCRF System Audit and SEBI CSCRF Cyber Audit — looks like in practice. TL;DR: SEBI CSCRF is mandatory for all SEBI-regulated entities. It requires continuous compliance, formal system and cyber audits by CERT-In empanelled auditors, and documented controls across governance, technology, and people. Organizations that treat it as a checkbox risk penalties, reputational damage, and regulatory action. Professional SEBI CSCRF Compliance services help you build and sustain a compliant, resilient cybersecurity posture. 1. What Is SEBI CSCRF and Why Does It Exist? SEBI’s Cybersecurity and Cyber Resilience Framework (CSCRF) is a comprehensive mandatory directive issued by the Securities and Exchange Board of India. It requires all regulated entities (REs) in the securities market to establish, maintain, and continuously improve their cybersecurity posture. Built on globally recognized frameworks including NIST CSF, ISO 27001, and COBIT, CSCRF is adapted specifically for the structure and risk profile of India’s financial markets. The numbers behind why SEBI acted tell a sobering story: India’s Cyber Threat Landscape — The Hard Data India’s financial sector faced 135,173 phishing attacks in just the first half of 2024 alone — a rise of 175% over the same period the previous year, driven by AI-powered phishing campaigns and expanded digital adoption (Kaspersky via Business Standard, November 2024). In 2024, India recorded nearly 22.68 lakh cybercrime incidents, with financial losses jumping 206% year-on-year to ₹22,845 crore — and 2025 saw that case count climb further to 28.15 lakh reported incidents (Ministry of Home Affairs data, The Print, February 2026). Cyberattacks on banks and financial firms more than doubled in 2024, and 2025 saw over 248 confirmed data breaches across scheduled commercial banks, with a 15% surge in attacks targeting the financial sector specifically (Tripwire, 2025; Cyber Law Consulting, 2025). The average cost of a data breach in India reached USD 2.35 million in 2024, up 7.8% year-on-year (IBM Cost of a Data Breach Report 2024, via Fintech Singapore). CSCRF is SEBI’s direct response to this threat environment. Its five core pillars — Identify, Protect, Detect, Respond, and Recover — create a framework for building lasting cyber resilience, not just reactive security. Key CSCRF objectives include: Identifying and classifying critical cyber assets and their risk levels Protecting systems and data through preventive technical and governance controls Detecting threats in real time through continuous monitoring and alerting Responding to cyber incidents with documented, tested response plans Recovering operations quickly with minimal disruption and measurable RTO/RPO targets 2. Who Needs SEBI CSCRF Compliance? If you are registered with SEBI and operate within India’s securities market, CSCRF applies to you. The framework uses a tiered classification model based on systemic importance, transaction volumes, and organizational size — so compliance requirements scale with your risk profile, but they do not disappear for smaller entities. Regulated entities covered under SEBI CSCRF include: Stock Brokers and Sub-Brokers Depository Participants (DPs) Stock Exchanges and Clearing Corporations Asset Management Companies (AMCs) Portfolio Managers and Investment Advisers KYC Registration Agencies (KRAs) Research Analysts and Proxy Advisers Mutual Fund Distributors (where applicable) Whether you are a Tier-1 exchange handling crores of transactions daily or a smaller registered intermediary, non-compliance is not a viable option. The consequences include regulatory penalties, suspension of registration, and the kind of reputational damage that takes years to rebuild. 3. Why Do Organizations Struggle with CSCRF? This is the honest conversation that most compliance guides avoid. The gap between what SEBI CSCRF requires and what most organizations actually have in place is significant — and it exists for predictable reasons. Trap 1: “We have an IT team, so we are covered.” Having an IT team is not the same as having a cybersecurity compliance program. CSCRF demands documented policies, formal risk registers, vendor management frameworks, board-level governance structures, and audit trails. These go far beyond what routine IT operations produce. Trap 2: “We did a one-time audit last year.” CSCRF is a continuous compliance framework. It requires periodic SEBI CSCRF System Audits, ongoing vulnerability assessments, real-time monitoring, and regular policy reviews. A one-time audit gives you a snapshot — not a safety net. Trap 3: “We are too small to be targeted.” Threat actors do not always go after the biggest targets. Smaller intermediaries with weaker controls frequently become entry points into larger ecosystems. SEBI’s tiered framework covers smaller entities precisely because of this systemic risk. The result of these misconceptions? Gaps in governance, undocumented processes, unreviewed vendor access, unpatched vulnerabilities, and untested incident response plans — all of which surface painfully during a SEBI CSCRF Cyber Audit. 4. What Do SEBI CSCRF Compliance Services Actually Cover? Professional SEBI CSCRF Compliance services are not about filling out a regulatory form and filing it. They are about transforming your organization’s cybersecurity posture from reactive and ad-hoc to structured and resilient. Here is what a comprehensive CSCRF compliance engagement looks like in practice. Gap Assessment and Readiness Review Before anything else, a compliance partner will evaluate where you currently stand against CSCRF requirements. This honest baseline assessment becomes the foundation of your entire compliance roadmap. What this covers: Review of existing cybersecurity policies